Australian financial-services firms have strict, regulator-set deadlines for handling complaints. Miss one and it's a breach. Spreadsheets and inboxes rely on someone remembering, and the records hold some of the most sensitive information a customer ever shares.
Case study · Governance, risk and compliance consultancy
Regulator deadlines kept by the system, not by memory.
A compliance consultancy wanted one platform to run complaints and incident registers for its financial-services clients. Each firm needed to trust that its records were its own, and that no deadline would slip.
- Challenge
- Strict regulator-set complaint deadlines, very sensitive records, and many client firms to serve.
- What we built
- A multi-client compliance platform with complaints and incidents registers.
- Outcome
- Deadlines built in, each firm walled off in the database, and AI pre-fill with personal details masked.
- Scope
- Many firms on one platform, with a per-client deployment option.
- Status
- Rolling out
Challenge
The problem
What we built
One platform, many firms
- Deadlines built in. Each register knows the regulatory obligations that apply, and the clock starts the moment a record does.
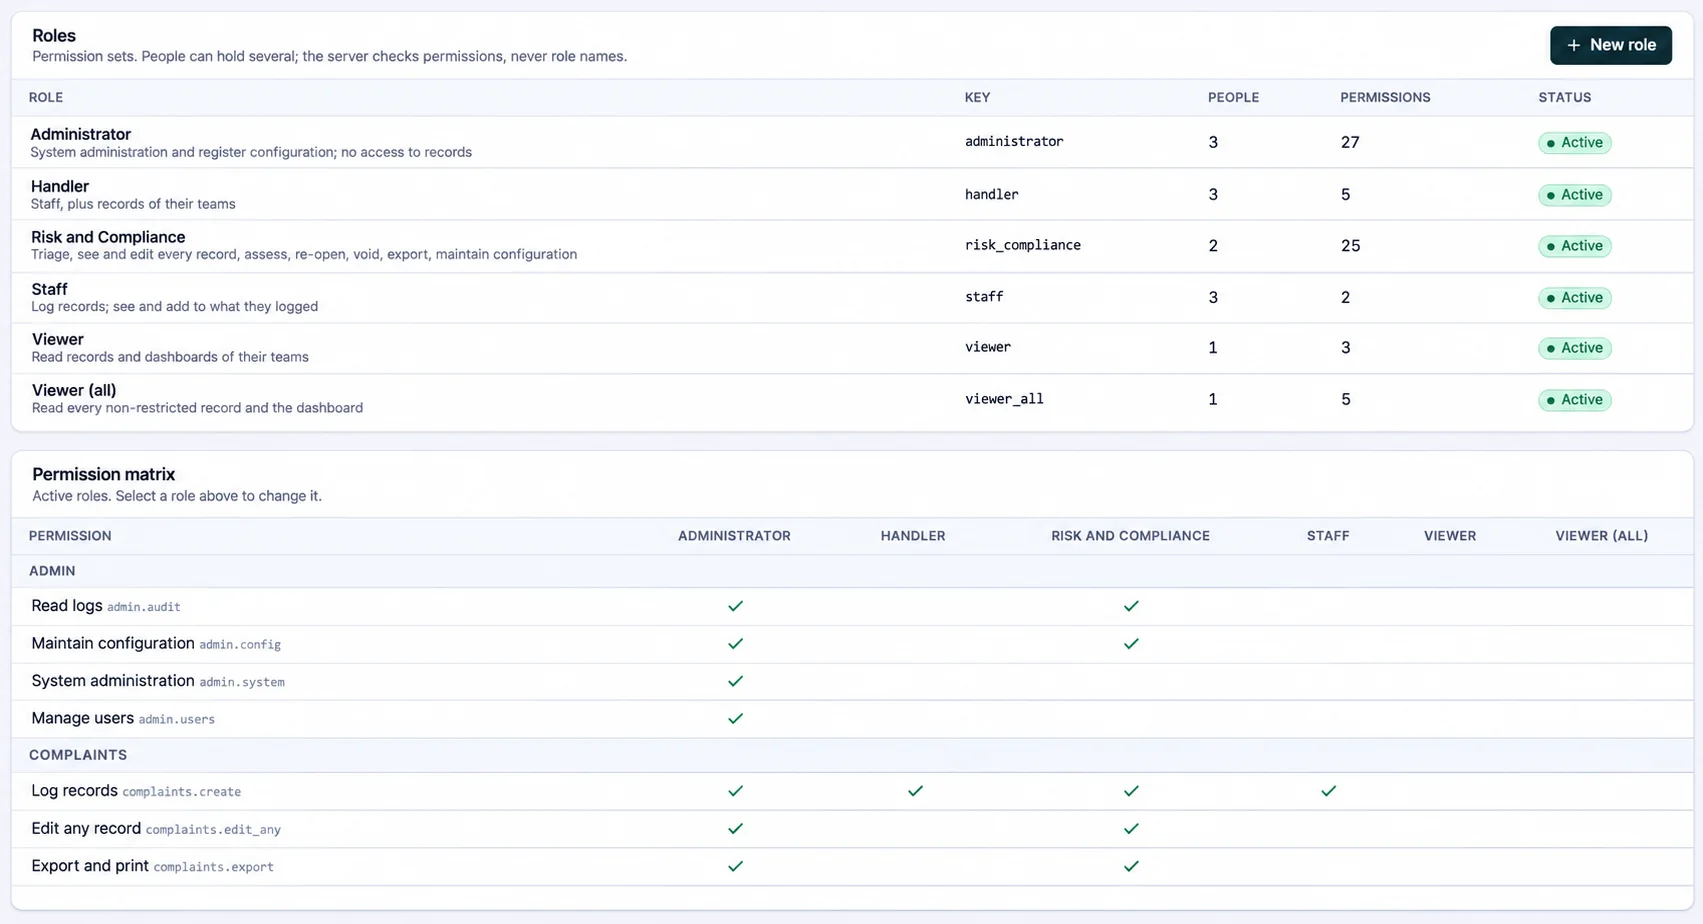
- Each firm walled off. No firm can see another's records, and the consultancy's own administrators can't read them either.
- Secure sign-in. Microsoft sign-in or a local account, with two-factor login.
- AI that saves typing. New records are pre-filled by AI, with personal details masked on our side first and only Australian-region AI providers used.
- Connected to the tools they already use, including their compliance-automation platform.
Status
Where it is now
The platform is being rolled out with the consultancy's first client, in a full rehearsal before it goes live, the same way we deliver every system. No outcomes are claimed until it is live.
In a regulated business, "we'll remember" isn't a process.
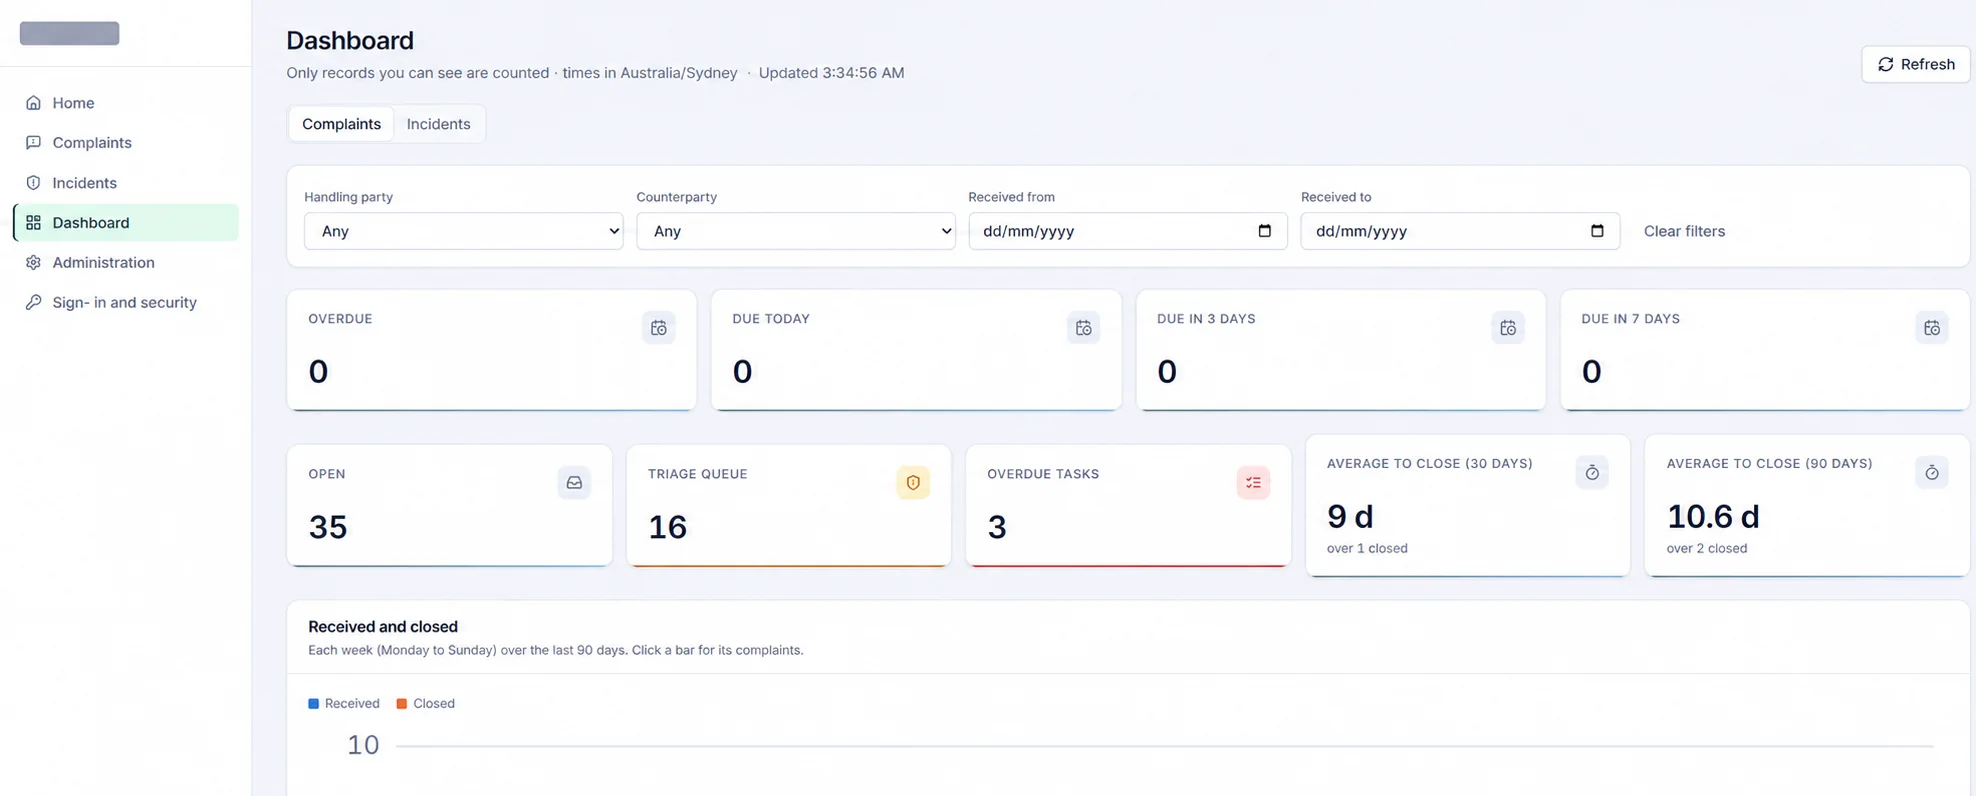
Inside the system
What it looks like in use
Compared with the usual way
Off the shelf, or built for the business?
A typical approach: spreadsheets and a shared inbox, or a generic case-management tool adapted to fit.
| Aspect | A typical approach | What we built |
|---|---|---|
| Regulatory deadlines | Tracked by hand, in calendars, custom fields or memory. | Built into each register: the clock starts with the record, and deadlines can't be missed quietly. |
| Many client firms | A separate workspace and subscription per firm, or one shared space and careful permissions. | One platform for every firm, with each firm walled off inside the database itself. |
| Who can see what | Administrators can usually see everything. | The platform's own administrators can't read any firm's records. |
| AI | A general chatbot, with customer details pasted straight in. | AI pre-fills records only after personal details are masked on our side, using Australian-region providers. |
| History | Records can be edited or deleted with little trace. | Record history and the audit trail can be added to, never changed. |
| When the rules change | Wait for the vendor's roadmap, or work around it. | A new obligation is a setting, not a rebuild. |
| Cost | Per-user licences for every person at every client firm. | One platform the consultancy runs for all its clients. |
Technical detail
For your IT team: what we actually built
A multi-organisation governance, risk and compliance (GRC) platform with complaints and incidents modules, configurable regulatory obligations and a per-client deployment option.
- Isolation in the database itselfEvery organisation's rows are fenced by row-level security enforced by the database, not just filtered by the application. A query without an organisation sees nothing.
- Platform staff can't read recordsAdministrators who create and manage organisations have no access to the records inside them.
- Obligations as configurationRegulatory deadlines (such as internal dispute resolution timeframes) are configured per register, so a new obligation is a setting, not a rebuild.
- Append-only historyRecord events and the audit trail can be added to but never edited or deleted.
- Local masking before any AI callPersonal details are detected and masked on our own servers before text is sent to an AI provider; only Australian-region providers are allowed.
- Sign-in and step-upMicrosoft Entra or local accounts, two-factor authentication, and step-up checks on sensitive actions.
- Signed releasesEvery release is a signed bundle; installs verify it before anything is deployed, with instant rollback.
- Encrypted backups with restore drillsBackups are encrypted, and restoring them is rehearsed as part of going live.
Tell us what's slowing you down.
Describe how things run today, or what worries you. We'll come back with a plain-English view: what we see, what we'd fix first, and roughly what it would involve. It's free, and yours to keep.